Exercise screenshots
These examples show what to look for. Use your own run as submission evidence.
Starting point
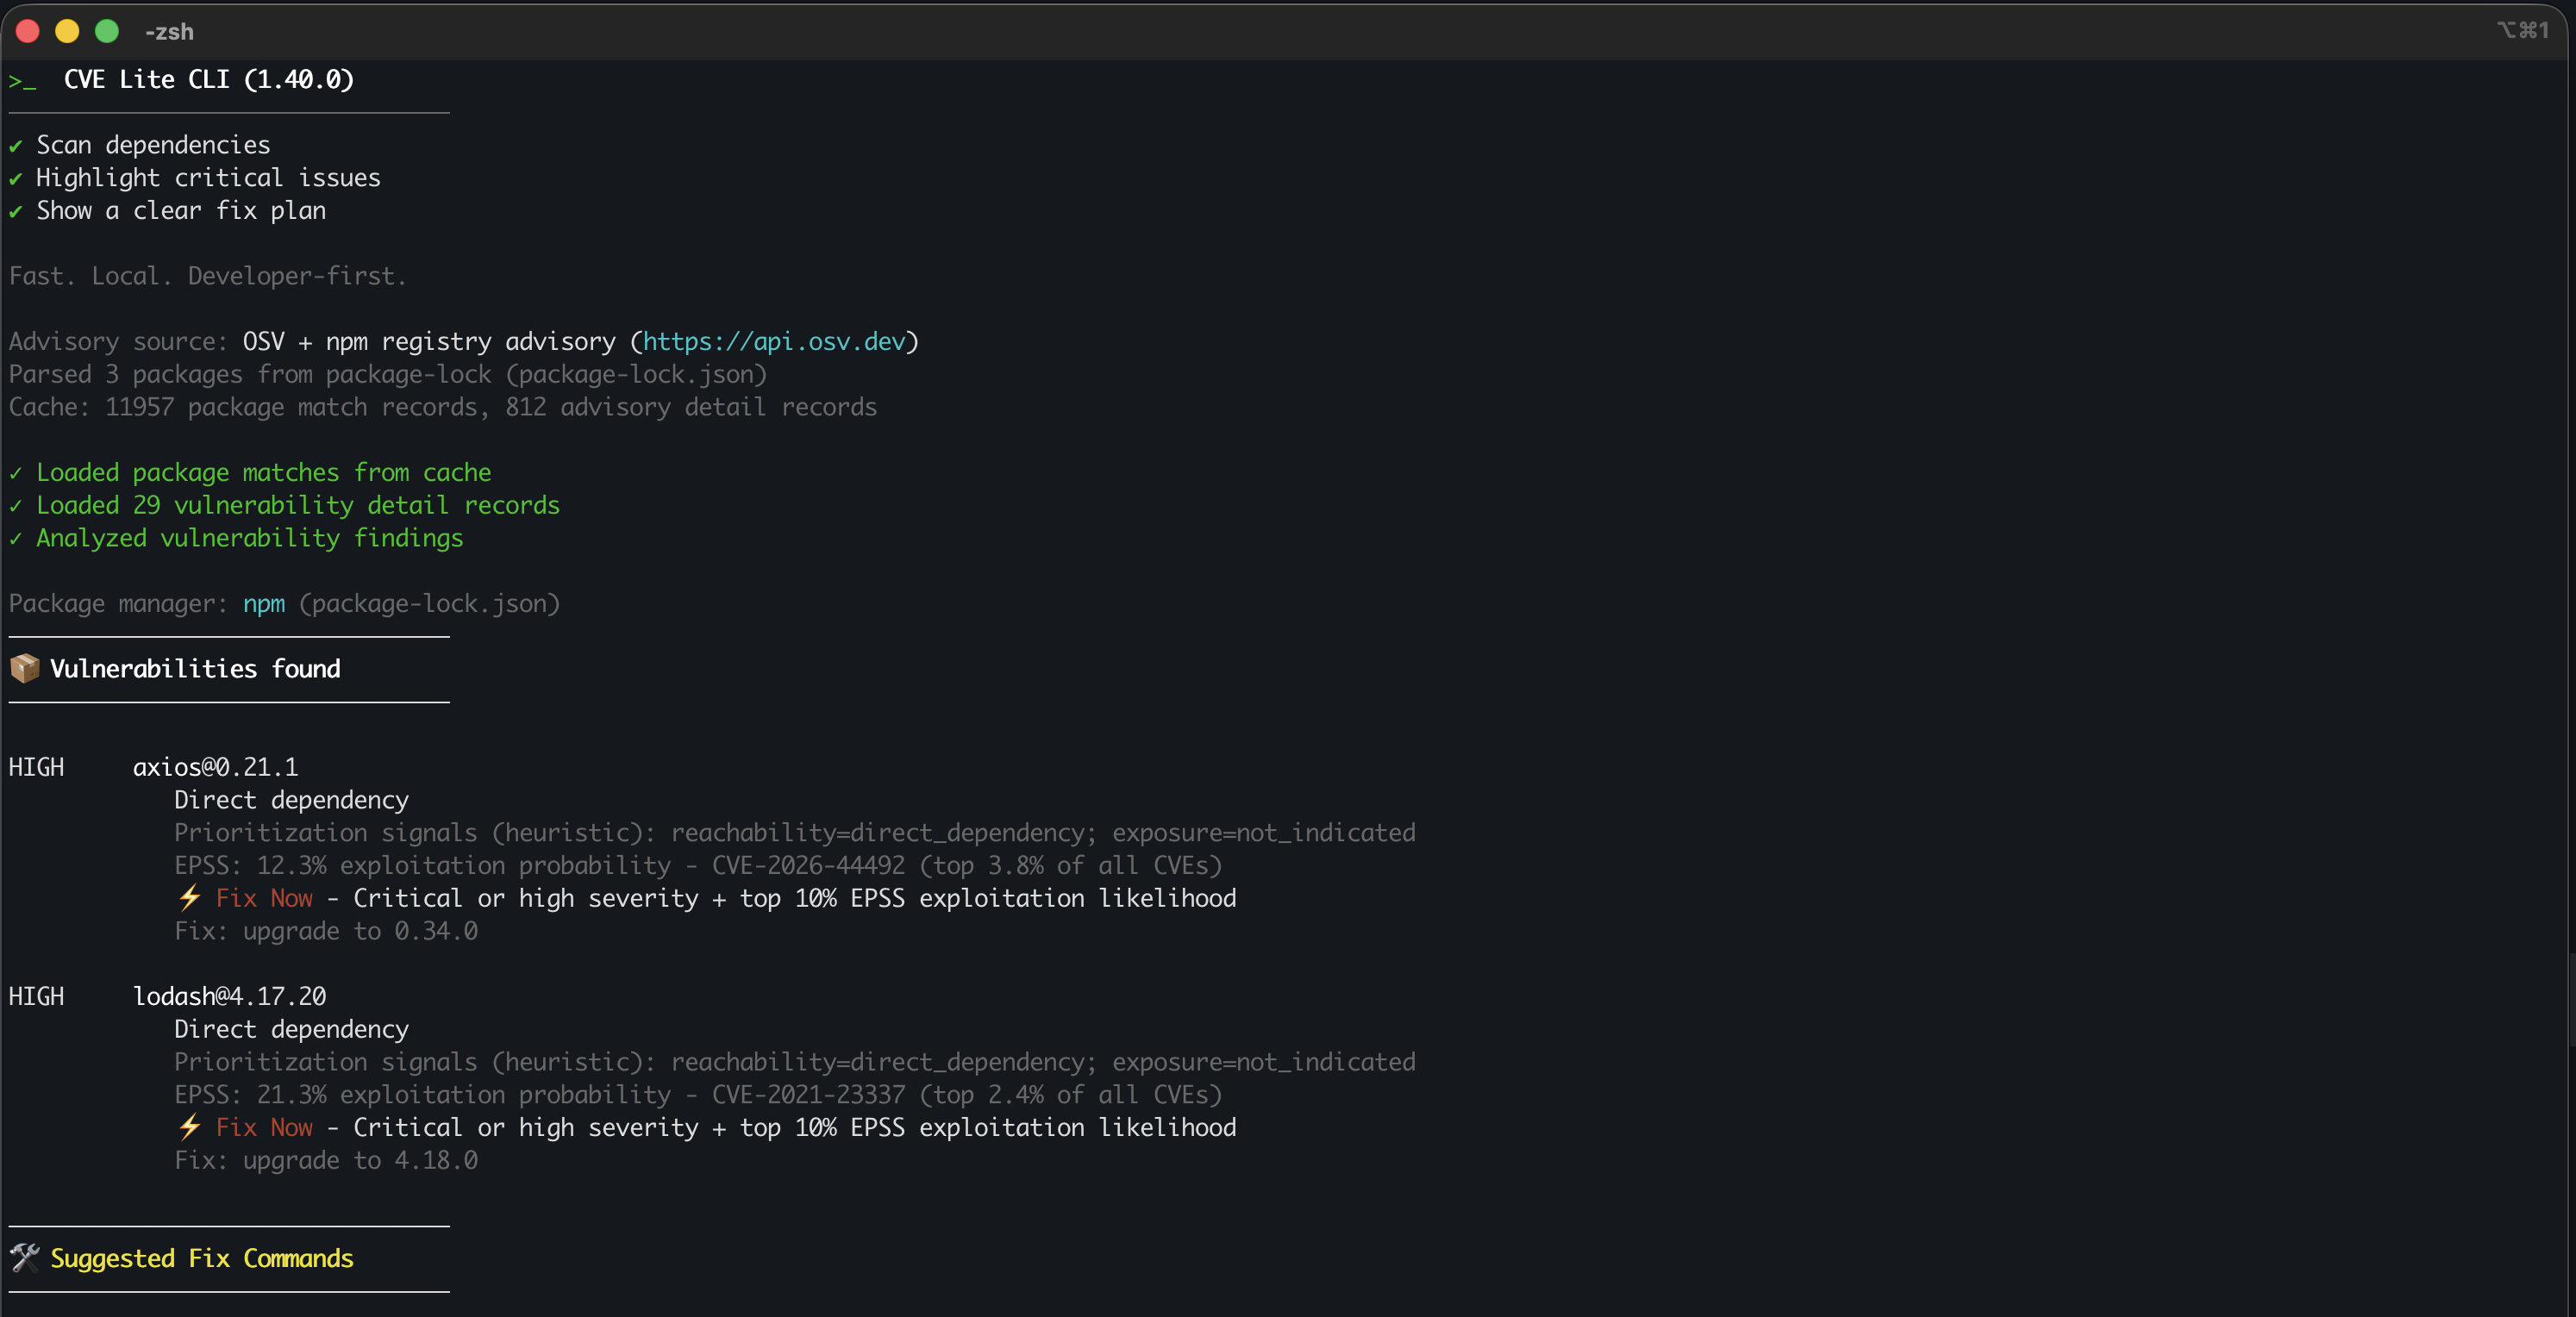
CVE Lite identifies the vulnerable dependencies in the supplied npm starter.
Fix guidance and scan summary
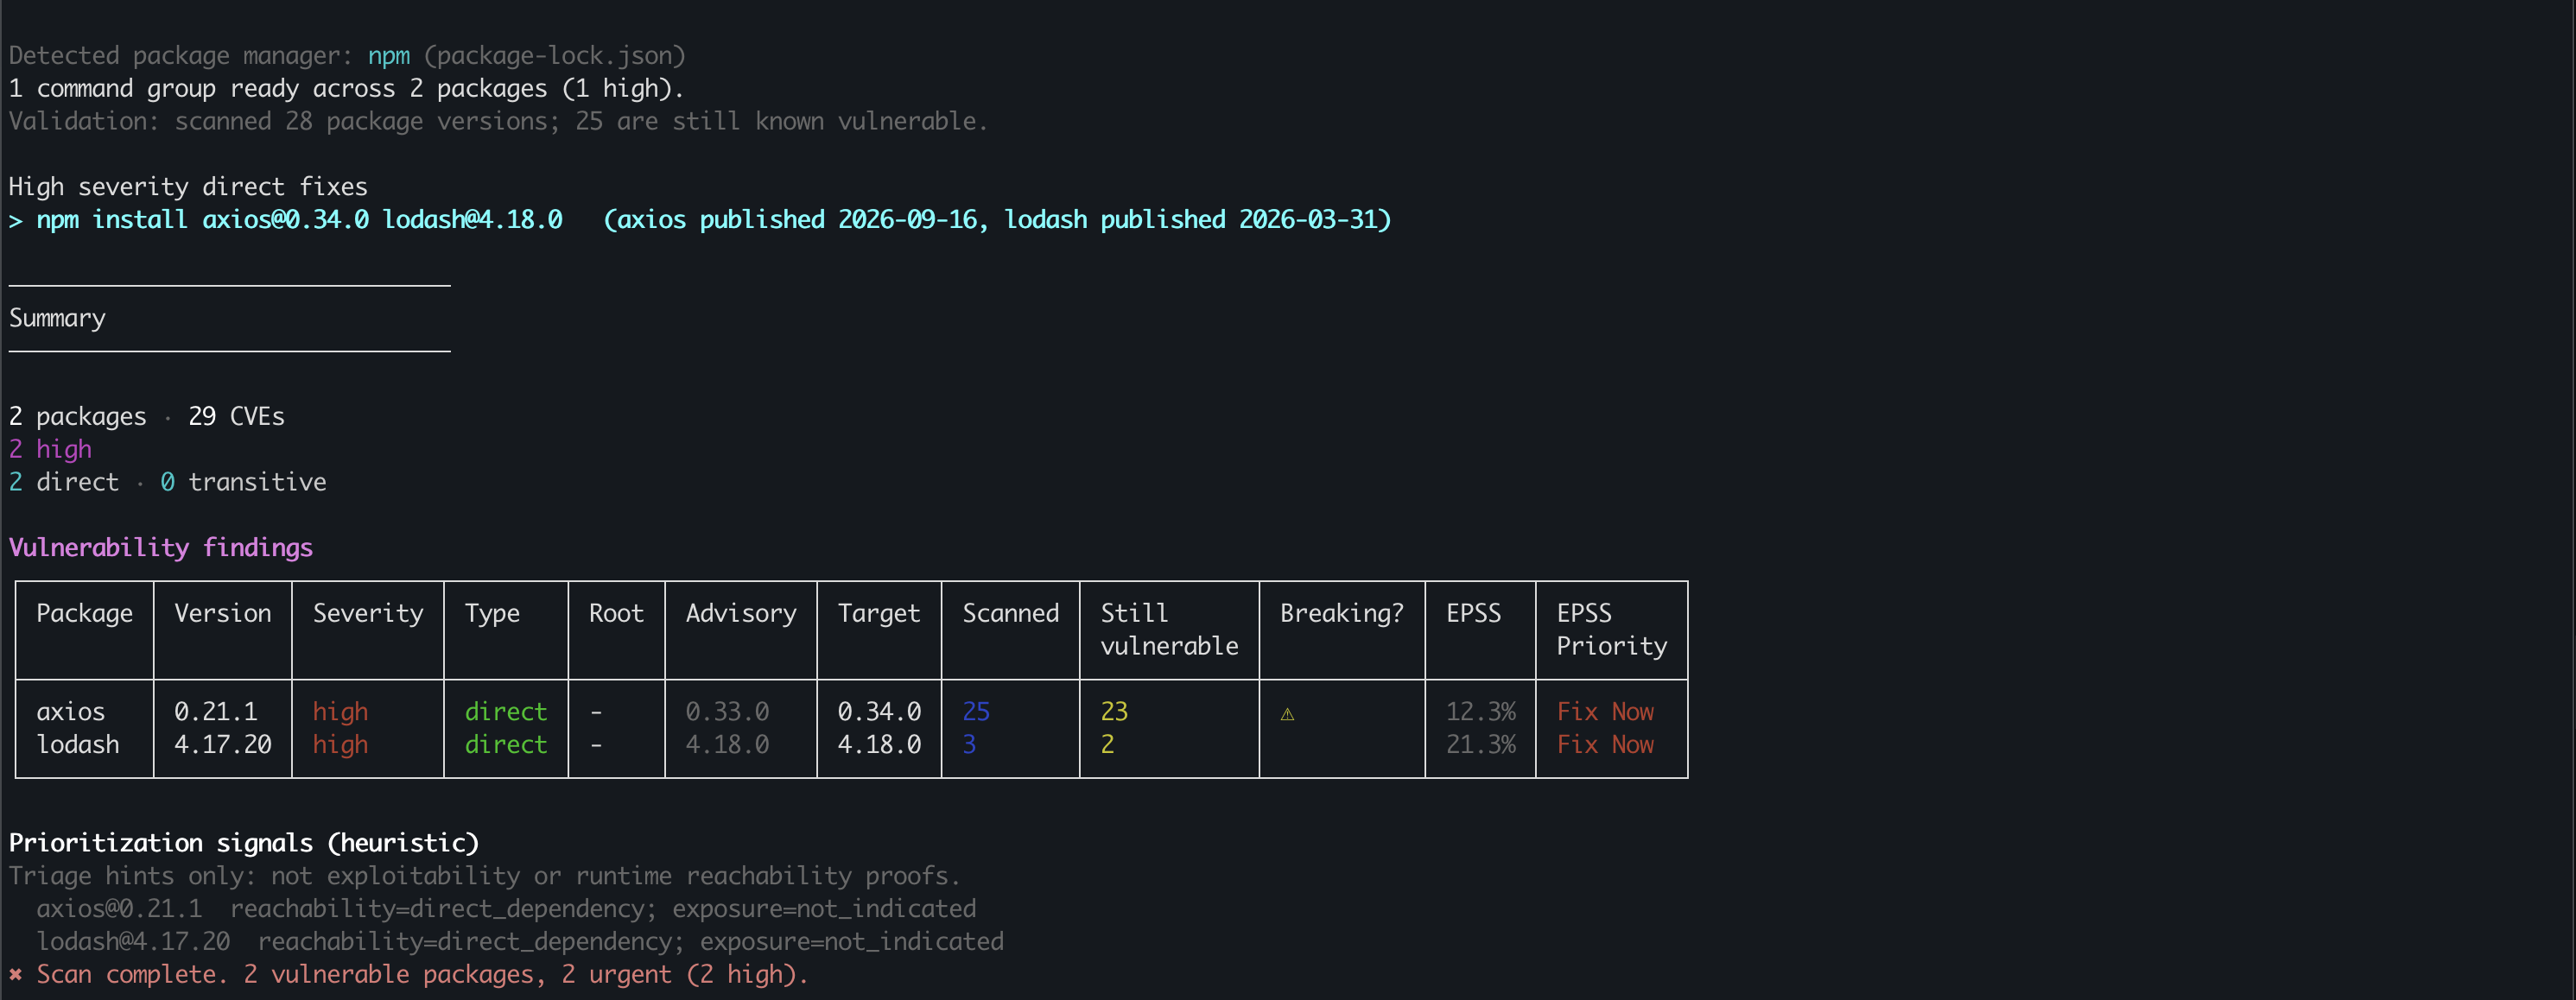
Read this second image after the first. It shows the same scan's recommendations and summary, not a repaired result.
After repair
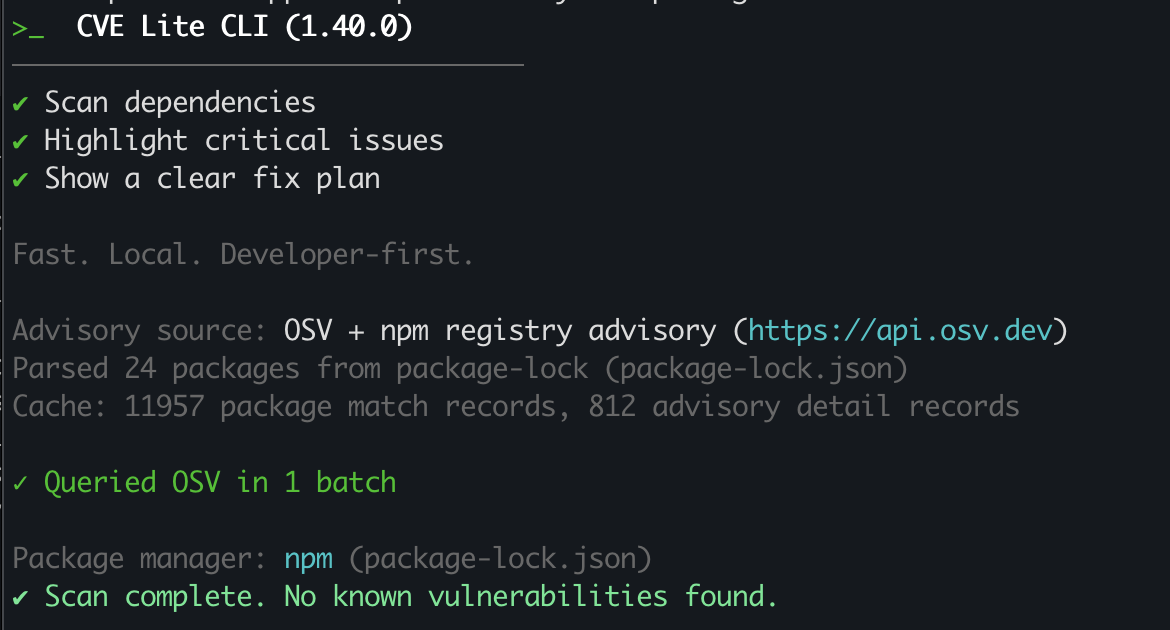
The scan parses 24 packages and reports no known vulnerabilities.
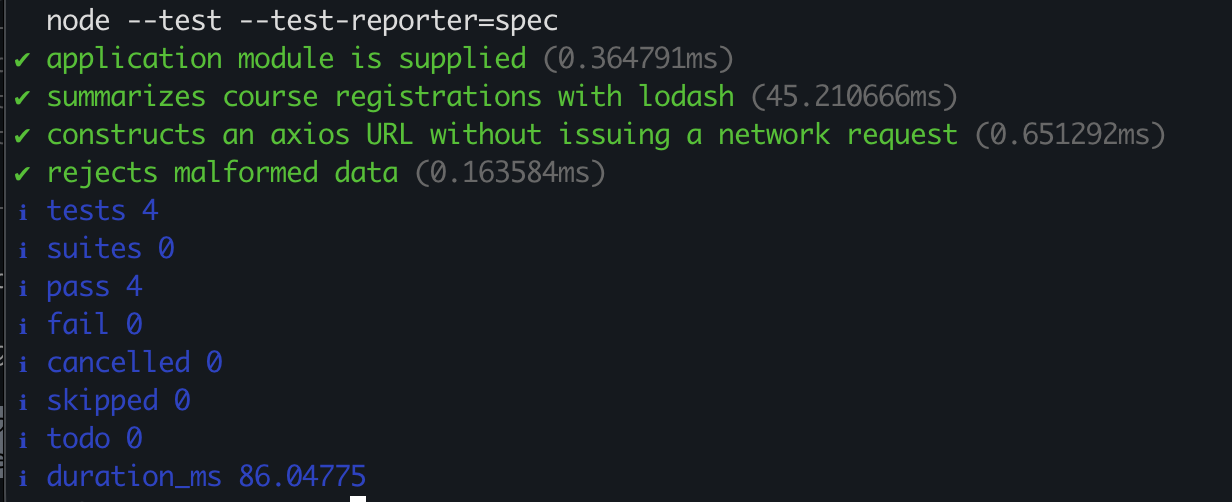
The actual output of node --test --test-reporter=spec shows four passing tests and zero failures. Follow the worksheet to record both tests and a rescan for your own repair.
Source
Actual terminal screenshots supplied by Sonu Kapoor on 30 October 2026, using CVE Lite CLI 1.40.0 and the npm starter. The capture used the independently exported terminal-02/app copy, which contains the same dependency application as Exercise 01. Command: npm exec --yes --package=cve-lite-cli@1.40.0 -- cve-lite . --all --no-open. The command omits --json to show human-readable terminal output; follow the worksheet's JSON command when saving structured evidence. Other package-manager tracks and advisory results can differ.