AI-Assisted Remediation
CVE Lite Classroom · Learn security by doing.
Classroom repository · CVE Lite CLI repository · CVE Lite website
Prerequisites: Exercise 01 or equivalent dependency-remediation knowledge, basic JavaScript, a terminal and one supported package manager. You should already be able to read a finding, justify a version change and verify a repair. Read the dependency primer first if needed (included as DEPENDENCY-BASICS.md in exported kits).
Allow about 30 minutes as a follow-on to Exercise 01, or 45–60 minutes for students with equivalent knowledge who are new to this activity. Setup, first-time tool familiarization and optional extensions need extra time. The supplied application is self-contained: no previous checkout is needed, but the knowledge prerequisites still apply.
Select npm, pnpm, Yarn Classic, Yarn Berry or Bun.
Read the worksheet, complete the submission, and follow the selected manager's setup. Instructor materials: walkthrough and rubric. Each manager includes a separate solution and historical before/after reports.
Example solution
Open the solution directory for the corrected apps across all five package-manager tracks, worked explanations, and instructor references.
Do not deploy this intentionally vulnerable app. The full safety and setup guides are at the repository root under docs; exported kits include them locally.
What the exercise looks like
Starting point

Authored sample advice for students to critique, containing intentional mistakes.
Expected result
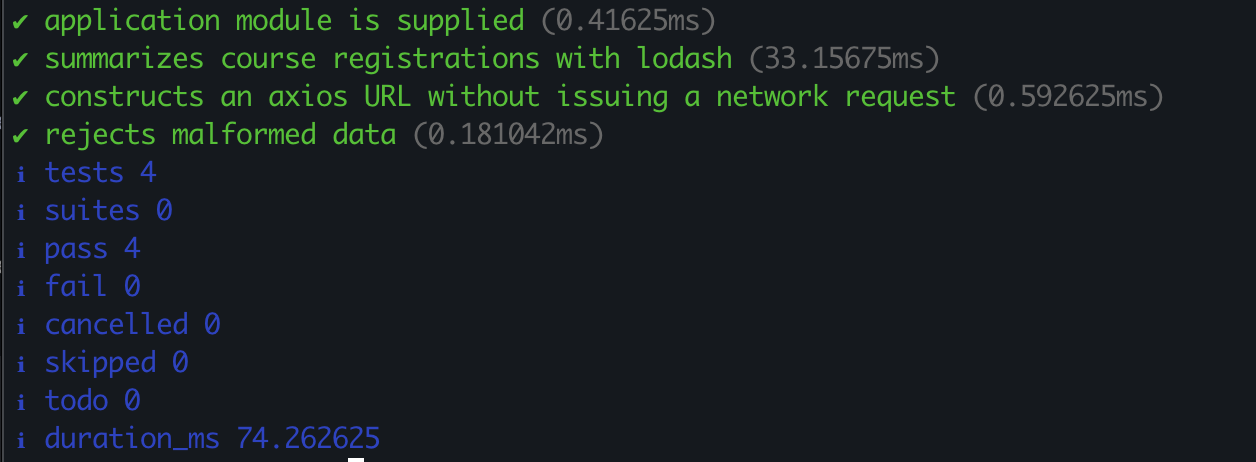
The application tests pass after the reviewed repair.
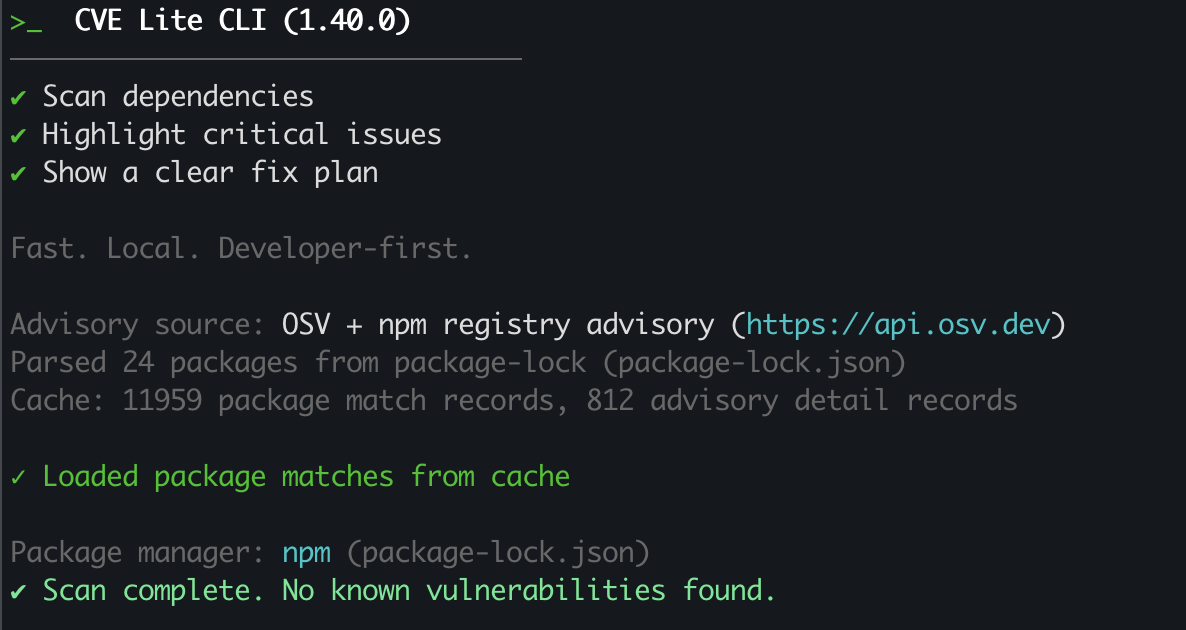
The completed rescan reports no known vulnerabilities. These terminal captures demonstrate independent verification on the exercise's no-AI-account route.
See screenshot sources and context. Use your own run as submission evidence.